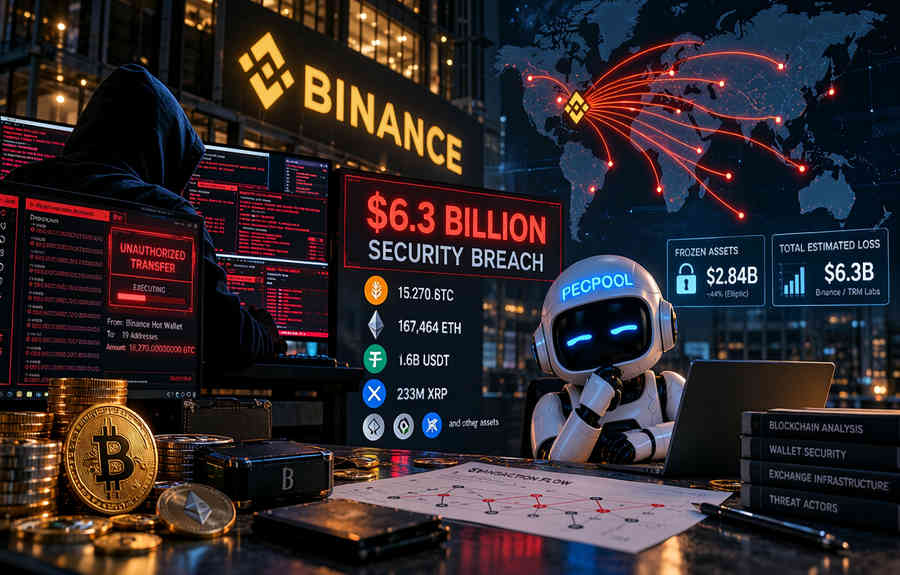
Binance has confirmed a security breach affecting approximately $6.3 billion in cryptocurrency across multiple blockchains. Investigators have traced the movement of 18,270 BTC and billions of dollars in other digital assets, uncovering evidence that the attackers may have compromised internal transaction authorization systems rather than simply stealing private keys. The incident has raised concerns over hot wallet controls, withdrawal infrastructure and the security of centralized cryptocurrency custody.
At approximately 20:05 UTC on October 29, five Binance wallets on the XRP Ledger began transferring large amounts of cryptocurrency to an unfamiliar address.
Within minutes, other Binance wallets were sending funds across several blockchains. By the time the exchange had suspended withdrawals, billions of dollars had left its operational wallets.
Binance confirmed the incident on October 30, estimating the impact at approximately $6.3 billion. Blockchain intelligence firms TRM Labs and Elliptic calculated losses of $6.36 billion and $6.43 billion respectively, based on their analysis of the affected addresses and asset prices.
Most of the stolen value moved in approximately 20 minutes, although additional transfers continued over the following hours.
Evidence of Advance Preparation
Investigators found indications that the attackers had begun preparing the operation at least 36 hours before the main theft.
According to TRM Labs, an attacker-controlled wallet received three small transfers from Tornado Cash on October 28. Software associated with the Ethereum component of the attack was subsequently deployed and tested against several wallets.
The final version was tested about four hours before being used against Binance.
The initial wave of unauthorized transactions involved approximately 233.46 million XRP. At around 20:20 UTC, a Binance Bitcoin hot wallet transferred 18,270 BTC to an attacker-controlled address.
Within the next few minutes, hundreds of millions of dollars in assets also left wallets on Tron and Ethereum.
The speed and coordination of the transfers suggest an operation involving more than a simple compromised withdrawal account.
The EIP-7702 Authorization Mechanism
One of the most technically significant parts of the attack involved a Binance Ethereum hot wallet known as Binance 14.
Investigators found that the attacker had used EIP-7702, a feature introduced in Ethereum's Pectra upgrade that allows a regular account to delegate certain operations to smart-contract code.
At approximately 20:20 UTC, the attacker submitted a transaction containing 50 previously signed authorizations.
Each authorization referred to a different transaction nonce, covering values from 18,914,775 through 18,914,824.
Because Binance 14 was actively processing transactions, its nonce was changing continuously. By preparing authorizations for multiple possible nonce values, the attacker increased the likelihood that one would be valid when the transaction was executed.
The authorization corresponding to nonce 18,914,809 matched. The other 49 did not take effect.
This allowed a malicious contract, often described as a sweeper, to execute transfers using the delegated authority of the Binance wallet.
At 20:24:23 UTC, approximately 167,464 ETH and 63 types of tokens were removed from Binance 14 in a single transaction valued at around $2.53 billion. The transfer included more than $1.6 billion in USDT.
The delegation remained active afterward.
Elliptic found that the attacker subsequently used the wallet's authority to move assets from another related account and repeatedly withdrew funds newly arriving at Binance 14. The final identified transfer through this mechanism occurred at 23:56 UTC.
The transactions on Bitcoin, Tron and other networks used ordinary valid signatures rather than the Ethereum delegation mechanism.
That distinction has become central to the investigation.
The Compromise of Transaction Authorization
Binance's preliminary investigation identified a potentially compromised laptop belonging to a DevOps engineer.
The exchange said that access obtained through the laptop may have allowed the attacker to reach a service container and submit unauthorized withdrawal requests.
Binance has also stated that it has found no evidence of leaked wallet private keys.
Nevertheless, transactions across several blockchains carried valid signatures, and the Ethereum delegation authorizations had been signed by the affected wallet.
TRM Labs believes the evidence is consistent with a compromise of Binance's hot wallet signing infrastructure.
This remains an assessment rather than an established root cause. Binance subsequently reported additional points of compromise but has not disclosed their technical details.
The central issue is therefore not evidence of broken blockchain cryptography. Investigators are examining how an attacker may have persuaded internal systems to authorize transactions that should never have been approved.
The Bitcoin Funds Were Split Across 19 Addresses
The theft included approximately 18,270 BTC, worth around $1.47 billion at the time.
The Bitcoin was initially transferred from a Binance hot wallet at approximately 20:20 UTC.
The attacker then divided the funds through a sequence of transactions known as a peel chain, eventually distributing them among 19 addresses.
Many of the resulting addresses hold balances close to 1,000 BTC.
According to Elliptic's October 30 investigation, the Bitcoin had not yet been transferred to a recognized exchange or other identified service at the time of its latest review.
The transactions remain publicly traceable on the Bitcoin blockchain, but the absence of a centralized issuer means there is no mechanism for an organization to freeze native BTC directly.
Stablecoin Freezes Interrupted Part of the Theft
The situation was different for stolen stablecoins.
Tether, Circle, Ripple and several other token issuers moved to restrict funds held at addresses associated with the attack.
Elliptic verified approximately $2.84 billion in frozen assets by October 30, or about 44% of its estimated total theft. Binance separately reported that approximately $3 billion had been frozen.
The attackers had already begun converting stablecoins into native blockchain assets before some restrictions took effect.
On Ethereum, approximately 434 million USDT was exchanged for 160,451 ETH through decentralized exchanges and liquidity providers.
On Tron, approximately 234 million USDT was converted into TRX.
Investigators also identified an Aave position involving about $59.9 million in USDT collateral, against which the attacker borrowed nearly 19,762 ETH.
Some exchanges were executed at prices significantly worse than prevailing market rates, suggesting that the attacker prioritized speed over conversion efficiency.
The freeze operations limited access to a substantial portion of the stolen assets, but freezing funds is not equivalent to recovering them.
Separating Theft From Protective Transfers
Elliptic excluded approximately $169 million in additional outgoing transactions from its total theft calculation.
Those transfers occurred after Binance had suspended withdrawals but went to established addresses without a known connection to the attacker.
Investigators considered them consistent with the exchange moving its own funds.
This illustrates the difficulty of assessing losses during an active incident. Large outgoing transactions may be part of either an attack or an emergency custody operation, depending on their destination and authorization.
Binance's Compensation and Reserve Position
Binance says it will fully cover losses using corporate funds and its SAFU emergency reserve.
On October 30, CEO Richard Teng said the company had allocated more than $6.34 billion to replace affected assets. Approximately $5 billion was already held in the same cryptocurrencies involved in the incident, with the remaining amount being acquired through market and over-the-counter transactions.
The exchange maintains that customer balances are protected.
However, a CoinDesk review of Binance's October 1 Proof of Reserves found that some affected wallets had previously been included among the addresses backing customer balances.
Based on that earlier snapshot, CoinDesk estimated that the ETH reserve ratio could have temporarily declined toward 94% before replacement assets were taken into account.
That estimate does not demonstrate a permanent customer shortfall. Verification will depend on the exchange's updated reserve data and the completion of its compensation measures.
Binance has indicated that it hopes to resume withdrawals by November 1 and publish a full Proof of Reserves report by November 2.
In its updated announcement, Binance clarified that deposits remain operational while withdrawals are temporarily suspended.
Attribution Remains Under Investigation
TRM Labs has attributed the attack with high confidence to TraderTraitor, a hacking group associated with North Korea.
Elliptic has also identified transaction patterns and address connections consistent with previous suspected North Korea-linked operations.
However, the evidence does not yet constitute a final judicial determination. Binance has not publicly confirmed the identity of the attackers.
Implications for Cryptocurrency Infrastructure
The attack did not reveal a vulnerability in Bitcoin's SHA-256 algorithm or its consensus mechanism.
Instead, the available evidence points toward the infrastructure responsible for managing wallet permissions and transaction signatures.
That distinction extends beyond cryptocurrency exchanges.
Mining pools and other operators holding funds for regular payouts face similar custody risks, even when their core transaction processing or mining infrastructure remains fully operational.
Protecting private keys, restricting signing permissions, segregating payout infrastructure and limiting the amount of cryptocurrency held in online wallets are separate but closely related security requirements.
As of October 30, the on-chain record provides extensive details about the movement of stolen assets, but the precise intrusion path remains unresolved.
The outcome of the investigation will depend on identifying how valid transaction permissions were obtained and why the affected systems were able to authorize transfers on such a large scale.